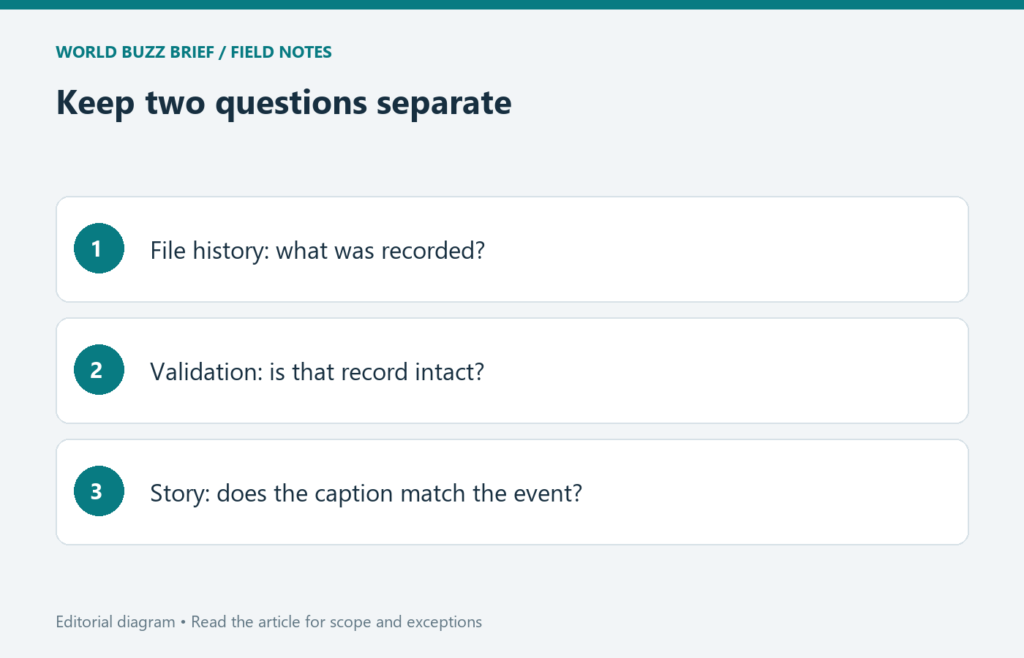
A valid Content Credential can add useful evidence about a digital image. It should not end the investigation into what the image is being used to claim. The practical distinction is between a file’s recorded provenance and the truth of a caption, event, or interpretation attached to it. Read the credential, then check the surrounding story separately.
Ask what the credential actually establishes
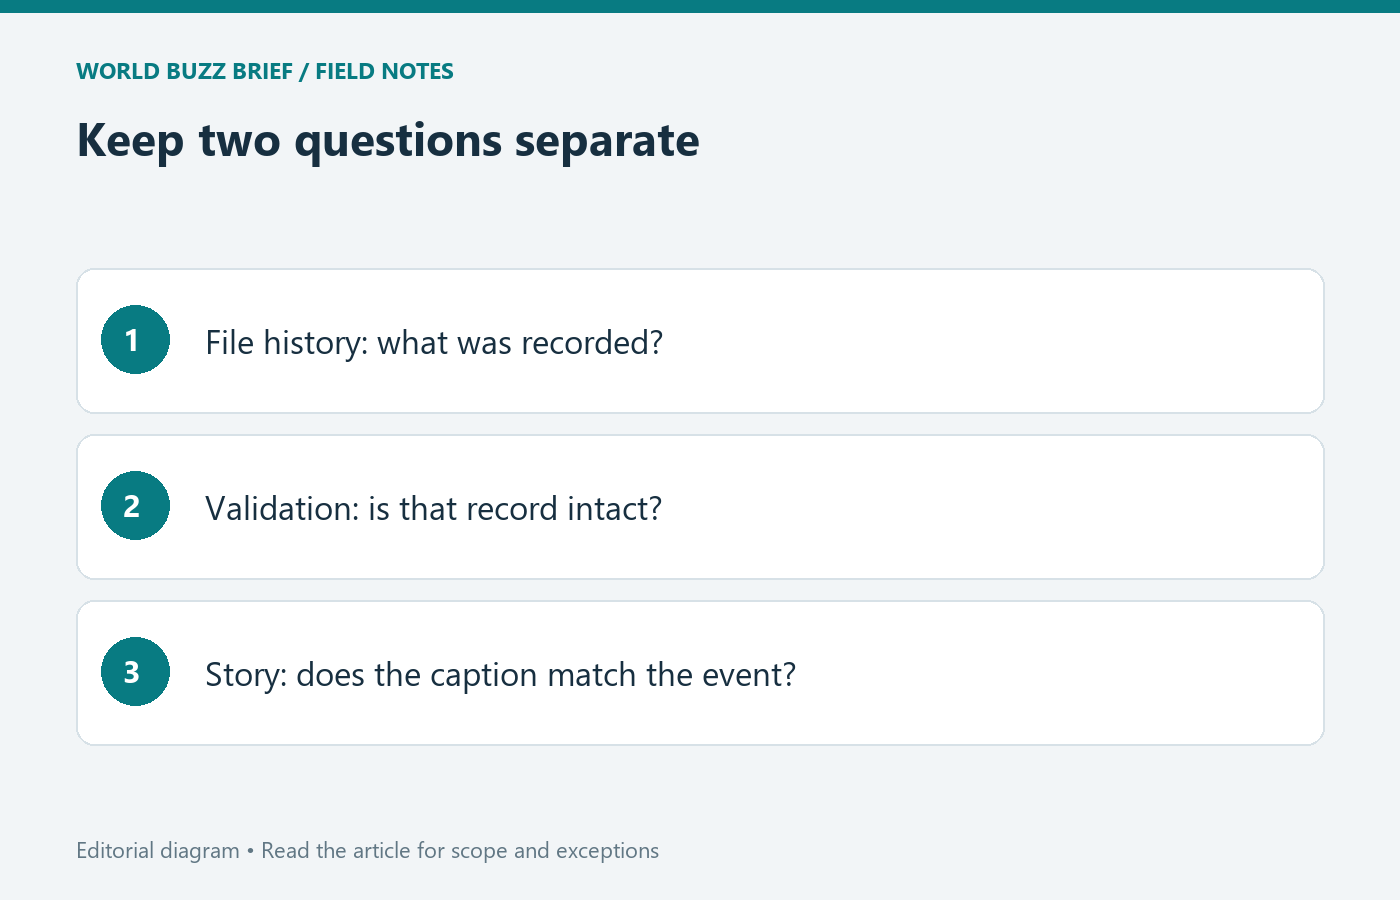
C2PA describes signed manifests that bind provenance information to an asset using cryptographic mechanisms. Validation can help show whether that recorded information and its relationship to the file remain intact. Start by reading the actual assertions and their scope rather than reducing the result to a green badge meaning ‘true photograph.’
Consider an illustrative case: an authentic image from an earlier event is reposted with a caption claiming it was taken today. Even an intact history would not, by itself, make the new caption accurate. The discrepancy concerns the claim being made with the image, not necessarily a change to the image’s pixels.
Check the chain you can actually inspect
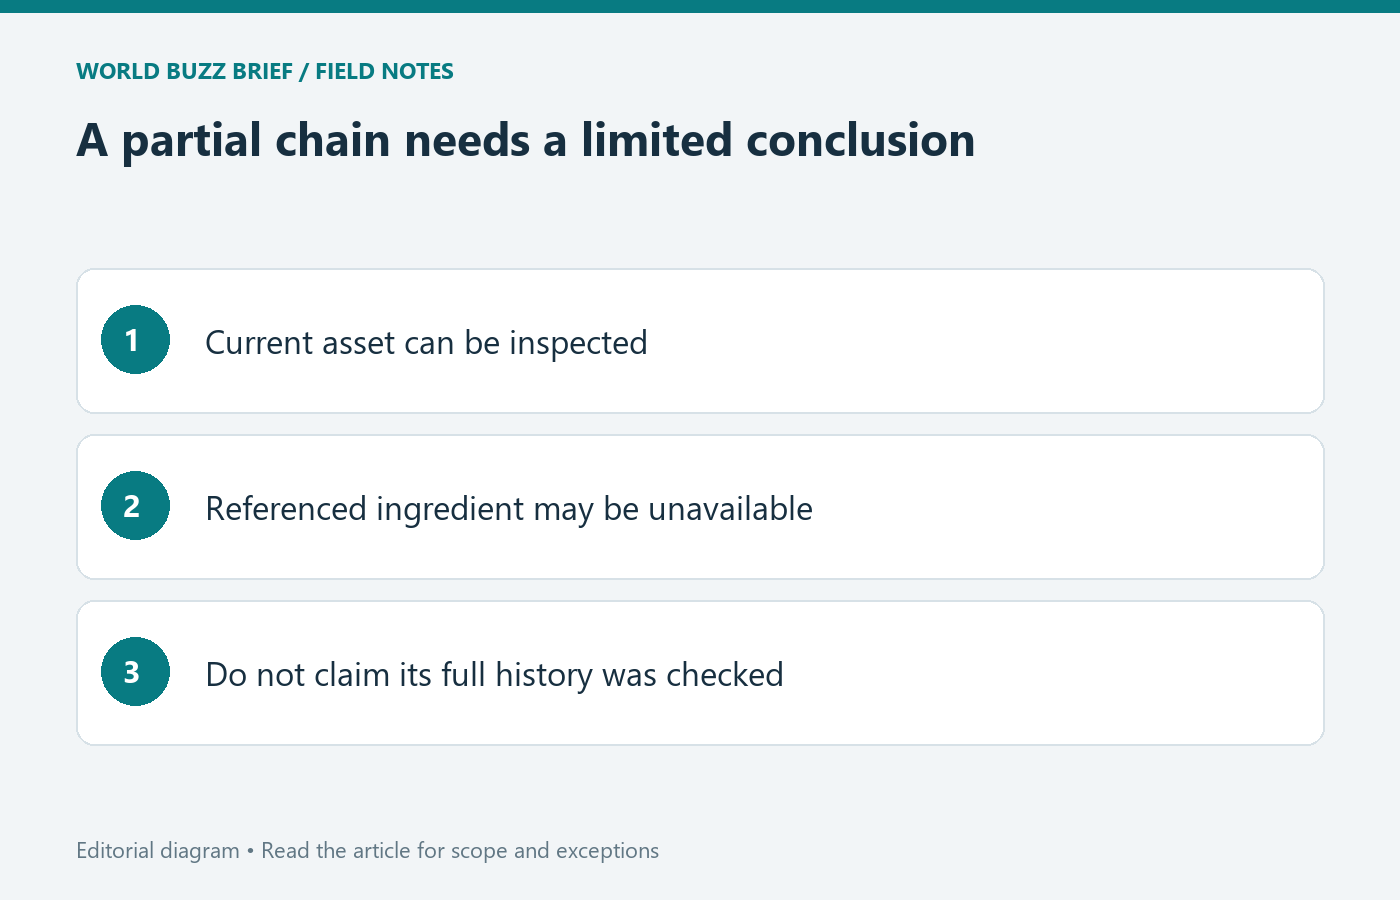
The C2PA FAQ explains that an asset can reference ingredients used in its creation, and that complete verification of those ingredients requires access to their data. A statement that an ingredient was previously checked is not identical to having its whole history available for your own inspection.
When reviewing an image, note what you can inspect directly and what is only referenced. If a composite includes material whose source is unavailable, say so. Do not turn a partial record into a complete story about every element. A useful conclusion can be narrower: the visible record validates, but a particular component’s full provenance was not accessible.
Treat missing credentials as missing evidence
Credentials can be separated from a file. C2PA describes soft bindings, such as fingerprinting or watermarking, that may help recover an associated record. The Content Authenticity Initiative also discusses how content-delivery transformations can strip metadata. These mechanisms explain why distribution matters when examining what reaches a viewer.
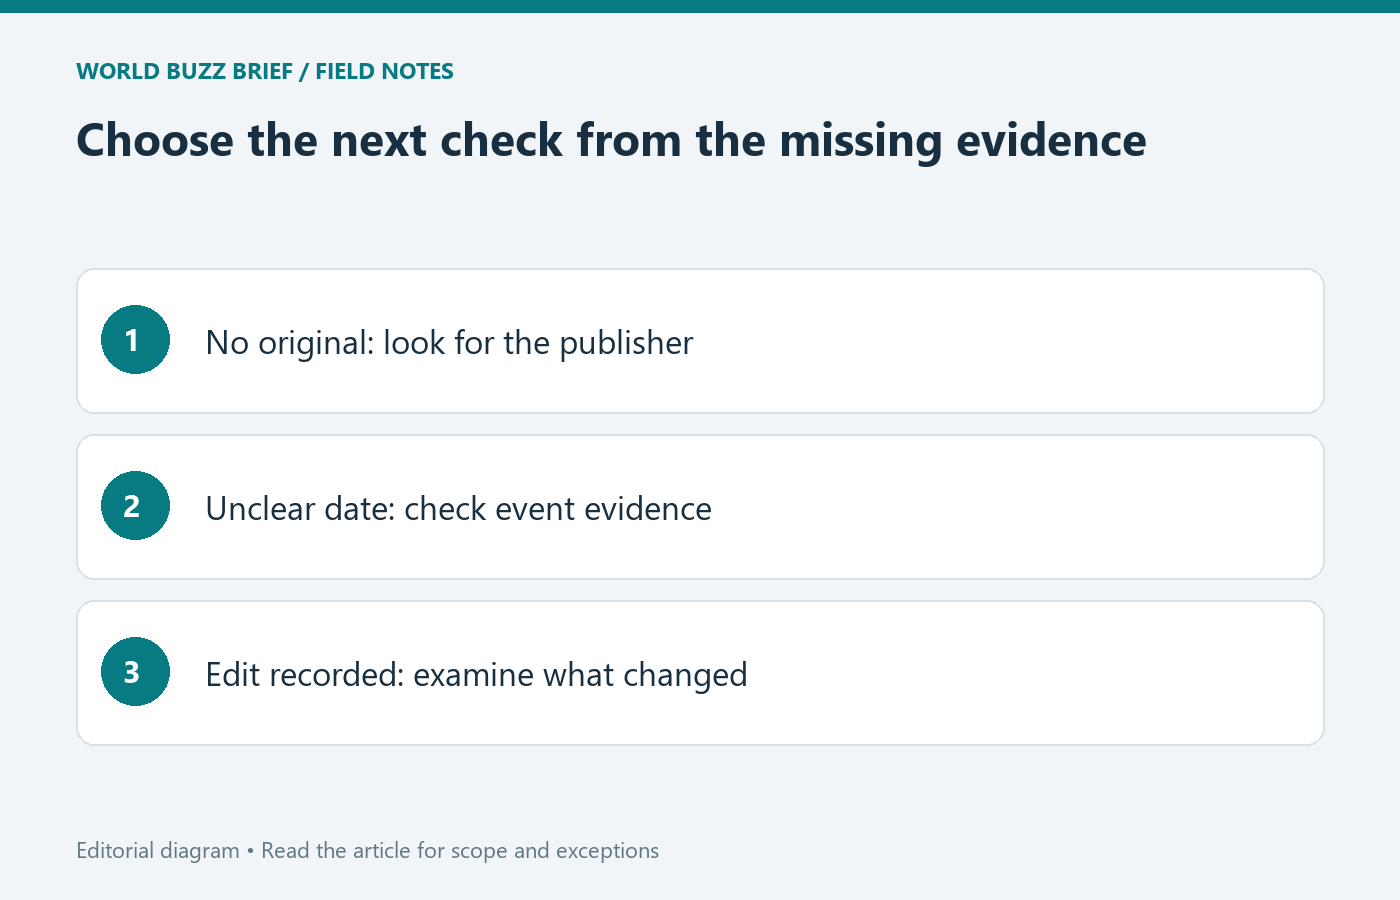
The inference is limited: absence of a credential is not, on its own, proof of AI generation or deception. Nor should a missing record be silently treated as a valid one. Look for the original publisher’s version and compare the available evidence; if you cannot establish provenance, retain that uncertainty in your conclusion.
Use two separate lines in your verification notes
Write one line for the file: what credential or history was available, what the validator reported, and what could not be inspected. Write another for the claim: who posted the image, what date or event they asserted, and what independent evidence supports that assertion. This prevents a technical validation result from accidentally becoming a fact-check of a news story.
For a reader deciding whether to share an image, the next action follows from the gap. An unavailable original calls for finding the source; an unsupported date calls for checking event evidence; an altered file calls for understanding the edit. A single badge cannot choose among those questions, but a carefully read provenance record can make the investigation more precise.